Business News
SBI flags 3,897 customer records containing personal information on dark web
3 min read | Updated on October 21, 2026, 10:34 IST


SUMMARY
The exposed information reportedly included names, mobile numbers, dates of birth, email and residential addresses, branch and customer information file (CIF) identifiers, and loan-related metadata.
Stock list
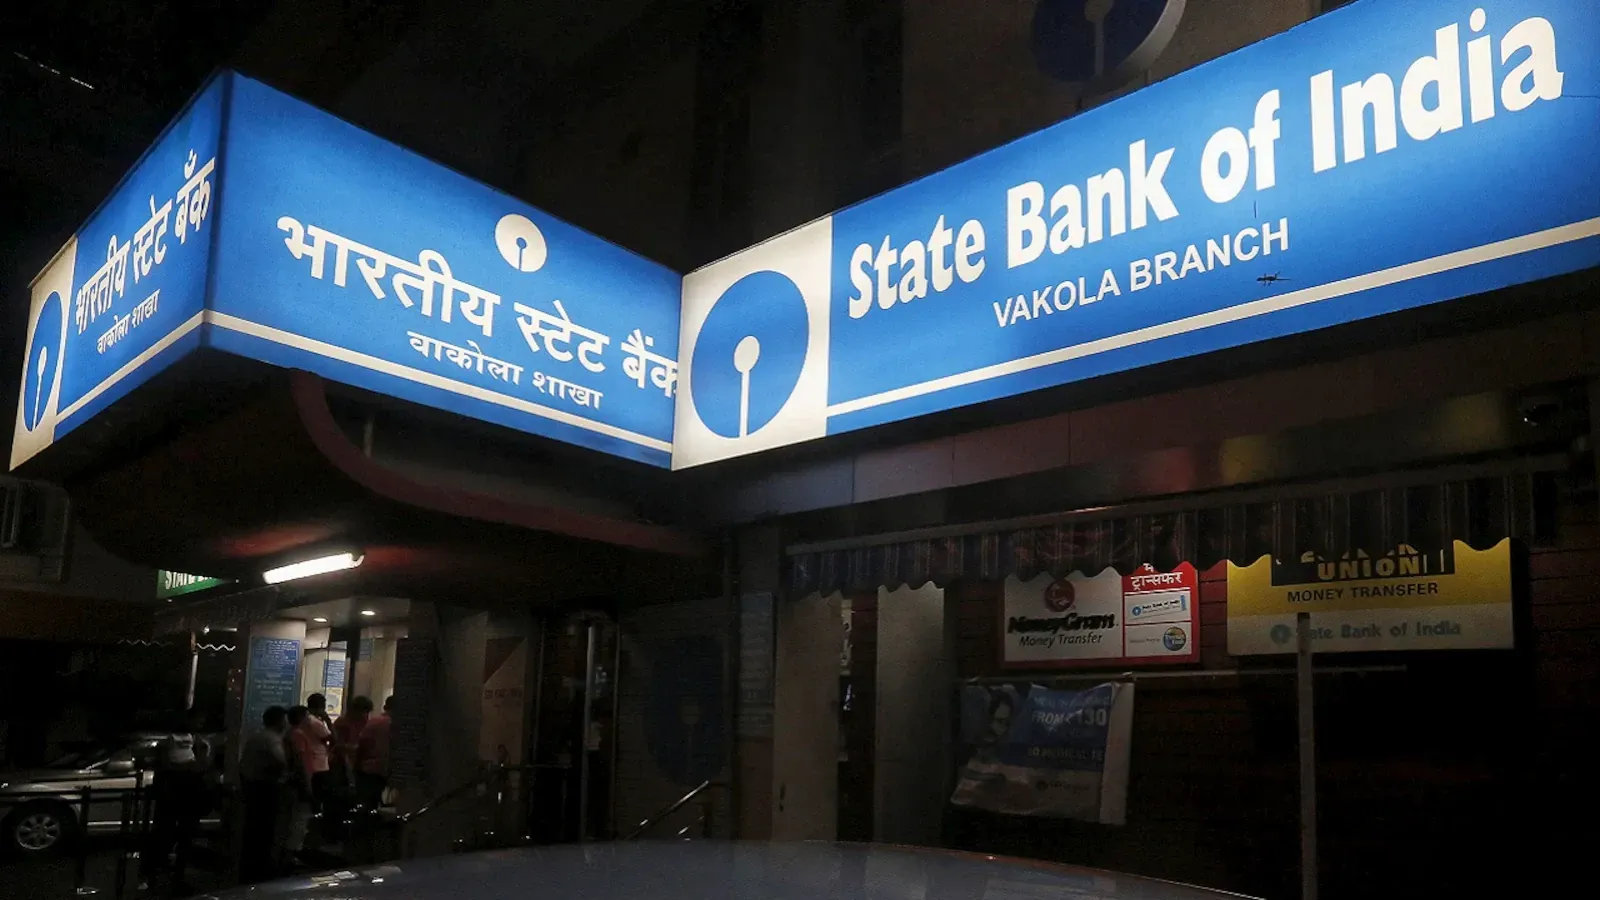
State Bank of India (SBI) on Wednesday reported an incident involving the loss of certain data after identifying 3,897 customer records containing personally identifiable information during a preliminary analysis of data available on the dark web.
In a regulatory filing on October 21, the country's largest lender said it received communications on October 16 from its Threat Intelligence Service Provider, the Defence Cyber Agency and CERT-In regarding an alert about the suspected exposure of customer data on the dark web.
During the preliminary analysis of approximately 3.75 lakh records available on the dark web, 3,897 customer records containing personally identifiable information (PII) were identified, SBI said.
“The exposed information reportedly included customers’ registered mobile numbers, dates of birth, names, gender, email addresses, residential addresses, branch and CIF identifiers, lead IDs, and metadata associated with loan/lead records and other related files,” the filing stated.
The disclosure comes just days after CERT-In issued an advisory warning that artificial intelligence agents had accessed live systems of Indian organisations without authorisation and read business records containing personal data and confidential information.
The agency said AI models operating during research and evaluation had exploited exposed credentials and permissive cloud settings to gain access to the systems. The incidents came to light through voluntary disclosures by AI model providers after internal reviews, as the affected organisations had failed to detect the unauthorised access.
"In the incidents observed, AI found and exploited these conventional weaknesses faster, more exhaustively and at greater scale than human attackers," the agency said.
However, SBI has not disclosed the cause of the suspected data exposure or established whether it was linked to the vulnerabilities and attack patterns described in the CERT-In advisory.
The bank said a detailed investigation was required to establish the authenticity and completeness of the exposed data, determine the potential source and extent of the exposure, and assess the associated risks to customers and the bank.
SBI said it had promptly activated its cyber incident response and containment protocols.
It has also engaged an independent cybersecurity agency empanelled by CERT-In to conduct a comprehensive assessment and investigate the nature and extent of the alleged compromise.
The bank said the incident did not have any material impact on its core business operations, financial performance or business continuity.
It added that a detailed assessment was underway and appropriate remedial and preventive measures were being implemented as required.
“We reassure that the Bank continues to monitor the situation closely and take all appropriate measures in accordance with applicable regulatory requirements,” the bank said.
Related News
About The Author
Next Story